8/20/2013

How to remove iLivid hijack browser, help to get rid of iLivid toolbar completely

Each time I open up a new tab, and then iLivid pops up, and there is also appear iLivid toolbar attached on my resent browser. I have tried to uninstall this program from my computer, but I cannot find this thing anywhere in my system. I am tired that I cannot get rid of iLivid by myself, so I appreciate someone will give me some tips to find out this program related files and registry.

please try to get rid of iLivid to keep your browsers safe. Download Popular Removal Tool Here to automatically remove  iLivid.


The first tip, before removing iLivid, you need to know what iLivid is.


iLivid is a unwanted program that can be installed on target computer without users’ consent, and when users search up “iLivid”, a lots of iLivid related folders downloading come up, and they have tried their best to click cancel promptly, but they cannot prevent it from getting the additional files about iLivid on computers. And the files finish downloading those files, users cannot right click "delete" on them, and then these files go off to the recycling bin. They feel happy that they have totally remove iLivid after emptying the recycling bin. However, when they search something on their browser address bar, the all the same exact folders are back. And it also can see on the Start Bar search, but these things cannot find in the "Uninstall/Change a Program".

Once iLivid gets inside the attacked computer, it will hijack the original homepage and browsers, and then add iLivid toolbar onto the search bar automatically. And then you find out a truth that you cannot delete the attached toolbar, and you reset your homepage to the default one but later it will change into http://www.ilivid.com/. Why such things happen, for iLivid can hijack your original homepage and replace your toolbar without asking your permission. In this part, iLivid is classified as a kind of browser hijack virus, which will change the default settings of your browser and homepage and toolbar. So you will get unwanted results and annoying redirections when you open a new search by using your default search engine. You can find that each time you search a thing on the search bar, and you will be redirected to iLivid or its related websites. No matter how hard try to terminate the redirections, but you find that it is too difficult to stop such things. And then you are leaded to the malicious websites which have relationship with this unwanted program, on those websites, you get a bunch of popup ads or certain links. Commonly, you cannot close those by click the X button on the right corner of the popping windows. In this case, your computer gains more opportunities to infect many threats, such as malicious, malware, Trojan.

8/17/2013

How to unlock European Cybercrime Centre Ransomware? steps to remove European Cybercrime Centre virus


My laptop has been locked by a virus called European Cybercrime Centre Ransomware, the locked screen of says Warning Your Computer Has Been Locked. I feel scared and need to ask several questions, and I hope someone will give me a response.


Question one, what website can help me to unlock my computer?

Question two, why this locked thing happens to me?

Question three, even if I sign in with safe mode with networking and safe mode with command prompt this locked screen pop up?

Question four, would the police who send the massage showing the screen come to my house and put me into jail after 72hours when it expired?


To solve the problems above, we need to know additional information about European Cybercrime Centre Ransomware.


Threat Level: Extremely dangerous

Number of Infections: 0-50 Files at one time

Geographical Distribution: Global

O S: All Windows Based PC, such as Window Xp, Window 7, Window8 and etc.

Affected Countries: USA, UK, Austria, Germany, Canada, Switzerland etc.


European Cybercrime Centre Ransomware is a very malignant and notorious infection which has been reported that it has attacked computer users expending to 30 nations according to the investigators said. In addition, these investigators also said that it was impossible to calculate the number of victims who attacked by this virus, and lots of Europeans said this virus can invade his or her own name in some commercial activities without their permission. Queries estimated by United States government that has received more than 1750,000 from computers users who are seeking advice on how to unlock their computers. In this case, we can know that infection is a big threat to the computer users all over the world.

How to disable Cloud-connect.net redirects, uninstall Cloud-connect.net virus

Interrupting with Cloud-connect.net redirect virus

Are you interrupted with Cloud-connect.net virus? If it is, you can see the following things when you are using the attacked computer. Please read this post carefully. Meanwhile, you can download the reliable Antivirus program Spyhunter here.

First of all, commercial pop-up notifications actively

To you show the basic sense of Cloud-connect.net infection that it is categorized as a nasty adware. For this reason, attackers could see a bunch of commercial ads popup on the screen. No matter what you are search on the internet, you should never pass to get the commercial notifications filling full of the searching web page. No doubt that Cloud-connect.net is an advertise platform that is responsible for showing up various ads on each web browser. Mostly, Internet Explorer, Mozilla Firefox, Google Chrome, Yahoo, Bing, and Safari are the common seen attacking browsers which can be highly used among the computer users. Whenever you search on the above browsers, you can catch many ads or certain links on the visiting web page.

Secondly, Cloud-connect.net redirect silently.

Once Cloud-connect.net redirects virus gets inside the target computer, it modifies the browser settings comprised homepage and default search engine without asking permission. As a result, your default homepage and search engine are hijacked, and the internal settings of browser. In
This case, many security experts have regarded Cloud-connect.net as browser hijacker which is found to be compatible with famous browsers contains Internet Explorer, Google Chrome and Mozilla Firefox. So each time you tab a new search or open a new site, you will be redirected to Cloud-connect.net its own web or its certain websites.

Why commercial advertising popup generate? Why Cloud-connect.net redirections keep happening?

Why those ads generate? The exact reason is that the publishers of those ads just want to earn money when users visit the websites which display pop-up ads within your browser and Flash update boxes. And the reason why you get annoying redirections to Cloud-connect.net or various sponsored websites is that the creators of this program the main goal is to collect much profit by increasing traffic of visiting views’ point.


Cloud-connect.net virus is distributed via several ways

There are some commonly used ways by Cloud-connect.net infection to run into the target computer. This virus can drop through visiting malicious websites and legitimate websites that have been compromised to unprotected computers. It is a kind of drive-by-download which happens surreptitiously. To open spam emails contain infected attachments or links to malicious websites is also a usual means used to propagate this type of adware. In addition, this infection can be installed manually by tricking the users into thinking they are downloading a useful application. In most cases, Cloud-connect.net threat is also famous on peer-to-peer file sharing websites and is often bundled with pirated or illegally acquired freeware.

Why I cannot keep Cloud-connect.net infection on my computer?

A.  Cloud-connect.net is a nasty adware that can display annoying commercial ads popups, attackers will get a bunch of ads when they are visiting the certain websites.
B.  It can affect many kinds of browsers which is highly using among computer users, including Internet Explorer, Google Chrome, Mozilla Firefox, Yahoo, Bing, and Safari.
C.  It modifies the browser settings comprised homepage and default search engine without users consent. After these changes happening, users cannot browse properly and normally.
D.  As a browser hijacker virus, Cloud-connect.net will hijack victims’ default homepage and search engine, and then lead those people redirects to its own sites or sponsor webs.
E.   Cloud-connect.net infection can run into the target computer via many means.
F.  This program is designed for earning money from users who don’t pay attention to search and install programs on line.
G. The threat is used by cyber criminals as a tracking website for affiliating programs and then sending important information to them.

How do I prevent Cloud-connect.net ads from popping up?

The best way to get rid of this virus is to uninstall this program manually, and the step-by- step process is needed to take care of. For this infection can come back again if you just remove it from Control Panel, and this virus can removed by antivirus partially. Please follow the following steps to delete this virus from your attacked computer.

Steps to remove Cloud-connect.net redirects from infected computer

1.    Stop all the running processes about Cloud-connect.net and then click End the process about this virus. (Please hold the Ctrl + Alt + Delete key together)

2.     Reset your browser’s settings (take Google as an example)
a.     Click on the icon ‘Customize and control Google Chrome’, select ‘Options’.
b.    Choose ‘Basic’ Options and change Google Chrome homepage to google.com or any other browser and then click the ‘Manage search engines…’ button.
c.     Choose ‘Google’ and make it your default search engine.

3.     Remove associated registry settings:
To finish this step, please be carefully to press Win and R key together. And type “regedit” and find out all related registry.

HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe
4.       Delete Cloud-connect.net popping up infected files:
%AllUsersProfile%\random.exe
%AppData%\Roaming\Microsoft\Windows\Templates\random.exe
%AllUsersProfile%\Application Data\~random
5.     In the end, please shut down your computer normally, and open it with normal mode, and then delete all cookies and history about this virus.


Notice: All manual steps are complicated, if you are not a computer savvy, we strongly recommend you downloading reliable removal tool – SpyHunter to keep your web browsers and system safe. 

Remove Cloud-connect.net with Powerful and Reputable Removal Tool 

SpyHunter is a powerful anti-malware program which is designed to detect and remove virus, malware, Trojan, worms and PUP. SpyHunter is one of few choices to clean PC that is infected with aggressive parasites.


Download SpyHunter Here (Official link and direct download)

http://www.pcresolvers.com/spyhunter.php


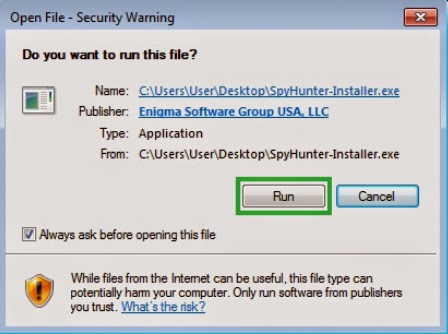
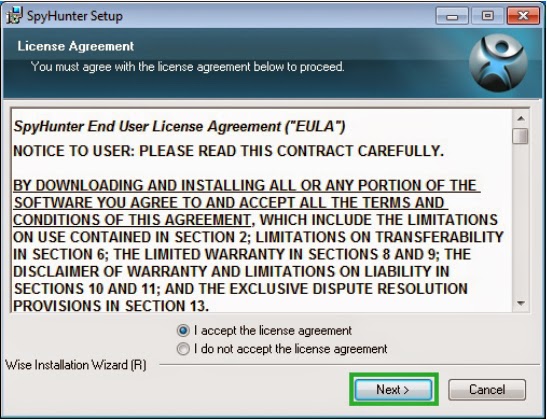
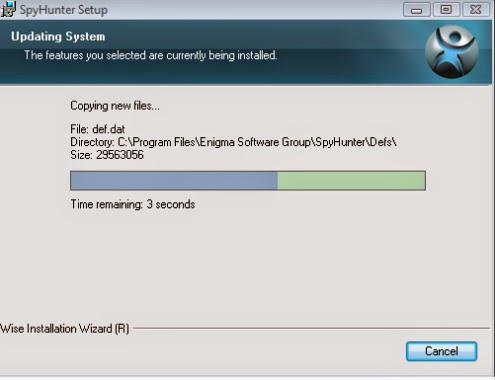
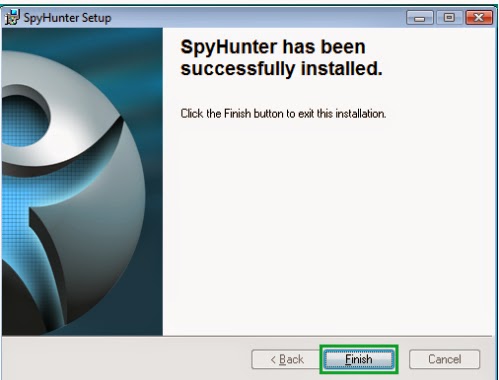
The following steps are installation process.
1. After finishing downloading, please search out the download file, and then open the file.


2. Follow the installation prompts shown on the screen to complete the installation.


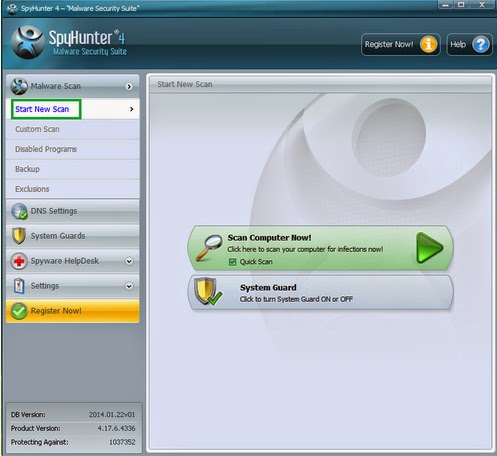
3. Scan your computer by clicking Scan Now button.


4. Remove all infected files detected by SpyHunter.


Pay attentions to: 
   Cloud-connect.net redirected virus can sneak into the compromised system without your consent, and this infection can utilize various means to spread. Once installed this virus, it begins to show annoying ads and popup notifications on your screen. And then it also can change the settings of attacked browsers and homepages, when you search by the infected browsers, you find that you are redirecting to Cloud-connect.net its own sites or other certain sites. In this case, you need to get rid of this infection as soon as possible. 

(Notice: Manual steps are difficult for you, you have to master good enough computer skills. we suggest you to download Cloud-connect.net virus removal tool to remove it quickly and safely.) 

Download Best Cloud-connect.net Scanner for Free Here!


Download Best Cloud-connect.net Remover Here!

8/16/2013

How to get rid of Search.installmac.com redirect from your browser completely

A nasty and stubborn Search.installmac.com has hijacked my browser address bar search


I downloaded Internet Explorer and a program called DJVu this morning, and I find that my Internet Explorer, Safari and Firefox have hijacked by a thing named Search.installmac, but exactly I don’t know what is this and why this thing happen. In fact, I consider this program as a Genieo product and it is a legal program. However, when I input any search into the address bar by using my Internet Explorer, Safari and Firefox, I find I automatically redirects to Install.mac.com page. I try to uninstall this program from computer, but I search on my computer, but I cannot find out any related to Install.mac or Genieo. I feel tired that these redirections made me crazy, and each time I type any words in the search box, I will get unwanted results into redirecting to Search.installmac.com without asking me. I have no any idea about this kind of things. 

Please read this post carefully. Meanwhile, you can download the reliable Antivirus program Spyhunter here.


A bunch of commercial ads from Search.installmac display


A part from the above things, I find out when you open my browsers, I can see a host of ads from Search.installmac pop up on my screen. Whenever I search any things on the internet, I can get lots of ads showing. Most of these ads are commercial products which have been curtained by the third parties who want to gain money from promoting these products. In this case, installmac can be use as a platform to display adverts. When you visit those ads, you may get chances to infect more threats onto the target computers. For this program can open a backdoor to other infections from outside.

Search.installmac sneaks into my computer stealthily 


I never notice Search.installmac before until I find myself keep redirecting to Search.installmac.com or its own certain websites. Really, I cannot find out how this infection can get into my computer, I never install it and download something related it. So I conclude that this program can run into target computers by such means, it may get into computer if you search online reckless, and if you don’t pay attention to quit some unwanted steps when install a program online. In addition, if you visit an unknown website or click any spam email and update software may catch this virus.


Free Download Scanner to Detect Search.installmac.com

What dangers will Search.installmac cause to my computer?


1.       It is a nasty and stubborn hijack browser which can hijack lots of browsers like Internet Explorer, Safari and Firefox.
2.       This is virus seems to be a product from Genieo and it looks like a legitimate program.
3.        It can lead I automatically redirects to Install.mac.com page whenever I type any search on the address bar.
4.       I can get a bunch of unwanted ads when I open my browsers, and those ads have been sponsored by cyber crooks who want to again money from promoting their products on this website.
5.       Search.installmac will sneak into the target computer without asking permission.
6.       It will tack your visiting history and collect important information from the attacked computer and then send them to the designers of the program.

Screenshot of  Search.installmac.com


The best way to remove Search.installmac.com from my computer


I have found that my antivirus cannot find this infection out, and I have tried myself to uninstall this program from my Control panel many times, but I still cannot remove it. When I open my computer, it comes back again, so I am confused, and I have no idea to handle with this issue.

To remove Search.installmac.com manually


Solution1. End all the related malicious processes.
Mean to open Task Manager;
Please press Ctrl and Alt and Delete key together to open the Task Manager, and then select referred processes with this infection, and then press End the process key.

Solution2. Stop any unknown startup items.
Way to stop: click Start menu and then choose Run, and type “msconfig” into the run box, and then open System Configuration Utility, and then Disable all possible startup items which has related with Search.installmac.

Solution3. Get rid of all associated with this infection from your browsers.
Solution4. To remove all related files as listing:

%AllUsersProfile%\random.exe
%AppData%\Roaming\Microsoft\Windows\Templates\random.exe
%AllUsersProfile%\Application Data\~random
%AllUsersProfile%\Application Data\.dll HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Random “.exe”
Solution5. Delete the added registry from Search.installmac:


HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run\[RANDOM CHARACTERS].exe
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings “CertificateRevocation” =Random
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\run\Random.exe
Solution6. Reset your browser’s settings. (Take IE as example)
Open IE, and then click Tools options on the tool bar, and choose Internet Options then open an Internet Options box, and in the General option, please reset the homepage to the default homepage.


All manual steps are complicated, if you are not a computer savvy, we strongly recommend you downloading reliable removal tool – SpyHunter to keep your web browsers and system safe.


Remove Search.installmac.com with Powerful and Reputable Removal Tool 


SpyHunter is a powerful anti-malware program which is designed to detect and remove virus, malware, Trojan, worms and PUP. SpyHunter is one of few choices to clean PC that is infected with aggressive parasites.


Download SpyHunter Here (Official link and direct download)

http://www.pcresolvers.com/spyhunter.php


The following steps are installation process.
1. After finishing downloading, please search out the download file, and then open the file.


2. Follow the installation prompts shown on the screen to complete the installation.


3. Scan your computer by clicking Scan Now button.


4. Remove all infected files detected by SpyHunter.


Suggestions: Search.installmac.com is tricky adware that will display lots of malicious ads, sponsor links, illegal websites. Once this virus enters into the target computer without asking permission, it will begin to do lots of annoying things. Annoying Pop-Ups, slow computer performance and steal privy data and so on. So please remove this infection from attacked computer immediately. And if you have no idea about how to handle with this program,Download the most popular antivirus program here to help you.


BEST WAY TO KEEP PC SAFE AND PROTECT AGAINST UPCOMING THREATS WITH SPYHUNTER

How to uninstall PC Defender 360, how to remove PC Defender 360 rogue anti-spyware

Numerous infections are detected by PC Defender 360, should you believe the notifications?

Normally, as a hoax anti-spyware program, PCDefender 360 does the same things as other fake antivirus tools like systemdoctor 2014, system care antivirus. This bogus tool also displays a bunch of fake notifications that claim installed computer has been detected with system scanning which tells that system is found lots of spyware, adware, Trojans and viruses destroyed. It states PC Defender 360 has found out various threats on the target computer, and it also lists a lot of security breaches which may be exploited, and then makes many examples of damages caused by those breaches. In addition, PC Defender 360 also warns you firewall alert and security alert, which claim that iexplore.exe is infected with Trojan-Downloader.JS.Agent.ftu that will steal Private data by the third party and unknown program is scanning your system registry which is known as identify theft Hoax.HTML.OdKlas.a. If you see the things set forth like above, please be careful and ignore them. For scanning by PC Defender 360 is just a scam.

Asking for purchasing the licensed version of PC Defender 360 to eliminate all scanned threats 

As its traits saying, PC Defender 360 will help computer users to fix the problems like system has spam, bulky, and intruding ads, browser crashes and decreasing speed to access web page, personal information and bank details get disclosed by criminal activity behind your back. And to fix all the issues listed, users need to purchase the licensed version of PC Defender 360. A host of users have made mistakes to install this false application which they are asking to pay certain fee. But in the end they find that this is a misleading program that cannot fix the problems as it listed, and make the thing turn worse. In this sense, you should realize that it is a rouge tool which itself is a virus. So you see the warning, please don’t fall into it.

Why you easily trap into the scam of PC Defender 360?

The PC Defender 360 is a foxy a program that it can imitate actions of famous antivirus software and pretend to be a decent and legitimate antimalware tool, which cannot be easy to distinguish from other true antivirus programs. In addition, it can simply run into the target computer by your unconsciousness surfing the internet. 

Different invading techniques uses by PC Defender 360

PC Defender 360 can be caught on the busy net. It can use the vulnerability security of computer’s user, when you are clicking unsafe and infected websites or installing the programs from insecure resources, you may get this infection. Mostly, this virus can spread through Trojan horses which will look for all possible leaks for system. In addition, this program can be bundled with other freeware, if you install any of those free applications, you may catch this infection.

Here is the screenshot of PC Defender 360.

 It is extremely dangerous to keep PC Defender 360 on your computer

One, PC Defender 360 is classified as rogue antispyware.
Second, this program can display annoying security alerts popup, and you find that computer screen is flooded with messages.
Three, it is misleading program which imitate actions of famous antivirus software and pretend to be a decent and legitimate antimalware tool.
Four, it begins to do a full scan of your system once you launch computer and then claim numerous threats on your computer. In addition, you are asking to pay a fee to buy the licensed version of program.
Five, this infection can cause more viruses onto this system.
Six, this threat can help cyber criminals collect personal information and bank details and then send that information to them.
How to get rid of PC Defender 360 manually:
Firstly, remove PC Defender 360 program from Control Panel
1.    Go to the Start menu, and select Control Panel.
2.  Click Add or Remove Program, and then go to the remove listing program, and then click Remove key.


Secondly, stop all running programs connected to this program.
1.    Please hold Ctrl and Alt and Delete key together to open the Task Manager.
2.    In the opening Task Manager, please tick the processes to end, and then press the button of End the process.

Thirdly, delete the related files from start up.
1.   Go to the Start menu, and in the search box, please type PC Defender 360.
2.   And then delete all the items appear related to this virus’ files.

Fourthly, show all hidden files.
1. Close all programs so that you are at your desktop.
2. Click on the Start button. This is the small round button with the Windows flag in the lower left corner.
3. Click on the Control Panel menu option.
4. When the control panel opens click on the Appearance and Personalization link.
5. Under the Folder Options category, click on Show Hidden Files or Folders.
6. Under the Hidden files and folders section select the radio button labeled Show hidden files, folders, or drives.
7. Remove the checkmark from the checkbox labeled Hide extensions for known file types.
8. Remove the checkmark from the checkbox labeled Hide protected operating system files (Recommended).
9. Press the Apply button and then the OK button.


Fifthly, delete associated files:
%commonappdata%\ifdstore
%commondesktopdir%\PC Defender 360.lnk
Sixthly, remove associated registry entries:
HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\ifdstore


Remove PC Defender 360 with Powerful and Reputable Removal Tool 


SpyHunter is a powerful anti-malware program which is designed to detect and remove virus, malware, Trojan, worms and PUP. SpyHunter is one of few choices to clean PC that is infected with aggressive parasites.


Download SpyHunter Here (Official link and direct download)


http://www.pcresolvers.com/spyhunter.php


The following steps are installation process.
1. After finishing downloading, please search out the download file, and then open the file.


2. Follow the installation prompts shown on the screen to complete the installation.


3. Scan your computer by clicking Scan Now button.


4. Remove all infected files detected by SpyHunter.


Bear in mind that: PC Defender 360 is a rogue anti-spyware which can show annoying pop up security alerts, and do fake scan of attacked system, and then claim that a lot of infections have been detected on your computer, you are asking to pay a certain fine to buy the licensed version of program to clear up all the threats. In fact, this program is a virus itself, all the detections are false, so you need to prevent you from effecting paying the fee, and remove it as soon as possible. 

(Notice: Manual steps are difficult for you, you have to master good enough computer skills. we suggest you to download PC Defender 360 removal tool to remove it quickly and safely.) 


Free Download Scanner to Detect PC Defender 360

BEST WAY TO KEEP PC SAFE AND PROTECT AGAINST UPCOMING THREATS WITH SPYHUNTER

8/14/2013

How to Uninstall Antiviral Factory 2013 Rogue (Removal Guide)


Suffering Pop Up Warning from Antiviral Factory 2013


Warning one!

System Scan: Your computer has infected with various infections including viruses, adware, spyware, tracking cookies, Trojan, worm.

All those infections can cause dangerous damages: (1) system startup failures (2) permanent data loss (3) System crash (4) internet connection loss (5) system slowdown (6) infecting other computers on your network.

It is highly recommended that you remove all the threats from your computer immediately.


Warning two!

Protection Level: Low

Antivirus Protection

Antivirus protection has disabled. Your PC is unguided against most known viruses and may be infected. Click “Enable Antivirus Protection” to protect your PC and make secure your internet behavior.


Warning three!

To get rid of all the threats on your computer, please download or activate Antiviral Factory 2013. Do you want to perform these actions now?

Click Yes, to download official intrusion detection system

Click Yes, to activate Antiviral Factory 2013(Recommended)

Click No, continue unprotected (Dangerous)


Discovering a New Outbreak of the Antiviral Factory 2013 Rogue


Antivirus detects this infection as Rogue.Win32.AVFactory2013. From the above warnings, you can know that it is a rogue scanner application which can display a host of fake alert messages. It will scan the whole system after your starting your computer and then get fraud popuping messages. It tells you that your computer is not in the security protection and informs you to enable the antivirus protection, it seems normally, but if you click the button “Enable”, you install or activate this program on your system. Once this application runs into the system, it will block your real antivirus quickly. And it does a bogus full scan, and states your computer has been highly infected with various spyware, malicious, viruses. To clear up these infections, it recommends you installing or downloading Antiviral Factory 2013. And you need to pay a fine to buy a license version of this program. Many users feel scary that those infections may destroy their computers badly, so they decide to pay the money to get the right of installation. After do the recommended things it has stated, you find that the detected threats are still appear and even the amount of infections increase. In this case, you can know that these are false-positive or misleading scan results which send by this program. Please ignore all the scan results. For this program just designed for earn money from promoting this program, for they can get the money when users buy it. In addition, in the process of payment, you need to assume that all materials, information, data, text, or images, (collectively the "Materials") available, so need to input important information such as bank accounts, and passwords and so on. So the hackers can see the details and collect it.

How to Get Rid of Trojan:DOS/Alureon.A, How Do I Remove Trojan:Dos\Alureon.A


Scan reports infected with Trojan:DOS/Alureon.A have made some statements

The statements attacked by Trojan:DOS/Alureon.A are listing below:

Firstly, computer crashed and frozen needed to restart, after restarting, getting a blank while accessing boot and setup menu, but no operating system, and cannot see the boot Windows.
Secondly, MSE partially removed Trojan:DOS/Alureon.A, but the rest virus’ files location cannot be found and cannot clean up.
Thirdly, keep getting flagged to externally backup by antivirus and you find your antivirus has been turned off.
Fourthly, unable to set restore point to earlier date before infecting this virus and any restore point will no avail.
Please see some horrible examples attacked with Trojan:DOS/Alureon.A
“I tried the TDS Killer, all that did was get rid of this virus but a new one Alureon.B.. etc just kept coming back. Microsoft Security Essentials picked up the virus and suggested I kill it with Standalone system Sweeper (or some name like that). When I did a full scan the Standalone said it didn't detect any viruses.”
“I got a virus how to remove Trojan:DOS/Alureon.A it comes up in Microsoft security essentials but even after clean and restart it remains. Also Microsoft malicious software removal tool finds nothing. What can I do to get rid of this??? I have tried superantispyware and malewarebytes both found nothing so I uninstalled them.”

What Trojan:DOS/Alureon.A is?

Trojan:DOS/Alureon.A is dangerous Trojan horse which can bring more infections onto the target computers. As we all know a truth that Trojans can be used as a tool to spread other malicious, malware, or other Trojans. So this Trojan also can open a gate to other infections from outside. Commonly, this virus can bypass the antivirus software scan. In this sense, your antivirus cannot find anything referred to it. Most cases, this virus will duplicate itself and breed quickly in a short time. In addition, it can keep staying in the backstage without your consent. For this part, it will do a lot of things just like a stealer. It will rewrite the system information, and add new files and registry onto the attacked computer which make your system strange, and it also causes the host files missing or corrupt the system later. Moreover, it will track the visiting history and collect personal data and then send then to the hackers who can use that information onto the commercial purpose.