12/02/2014

"You've been hacked by the Syrian Electronic Army (SEA)" Pop-up – How to Remove “You’ve been hacked by the Syrian Electronic Army (SEA)” Pop-ups


Be adware of "You've been hacked by the Syrian Electronic Army (SEA)" pop-up


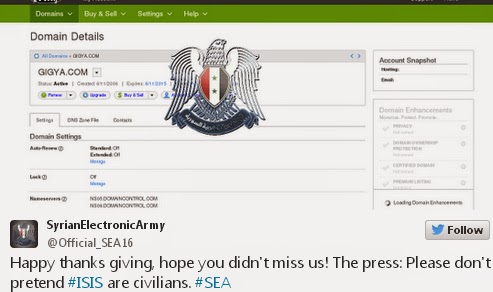
“The Dallas Morning News was one of several large media and entertainment websites to briefly be attacked on Thanksgiving morning by hackers identifying themselves as the Syrian Electronic Army.”


According to some computer experts’ sayings, some hackers took control of Gigya’s domain name and altered its settings to direct users to another websites. There is one important thing to know your computer is experiencing a pop-up from "You've been hacked by the Syrian Electronic Army (SEA)". As soon as you get accessed the affected websites Thanksgiving morning, they were greeted by a pop-up that read, “You’ve been hacked by the Syrian Electronic Army (SEA),” and then were redirected to an image of the group’s logo.

12/01/2014

How to Remove Generic5.ciuu – Completely and Easily Steps to Remove Generic5.ciuu


Generic5.ciuu was found, but can't make it stay away?


Generic5.ciuu has been installed into target computers without any tracing for users. It keeps showing on every window when users open and add/remove programs. This infection can use special code to hide deep into the infected system, so many users cannot uninstall it even though try to uninstall it from control panel. And they will get some error messages.

Fake Antivirus AVbytes Win 7 Pro 2015 Removal Step by Step – How to Remove Fake Antivirus AVbytes Win 7 Pro 2015


Reports about Fake Antivirus AVbytes Win 7 Pro 2015


Fake Antivirus AVbytes Win 7 Pro 2015 seems to be a very good and useful utility for computer, but it may act some behaviors on the installed computers. As a result, this program shows its disadvantages to computer users. Once installed, this program can do a scan on the target computers and then display many pop-ups with report for you. In the scan result, you are informed that your computer has some issues like virus or error which you need to fix it immediately. Even though you reboot your PC, another scan and pop-ups will show again. You may be asked to register the license of Antivirus AVbytes Win 7 Pro 2015 to fix the detected problems. But such pop-up messages are not trustful ones, so you have to uninstall this program from your PC as soon as possible you can.

Removal of rdsrv.com from IE/Chrome/ Firefox – How to Remove rdsrv.com Completely


You cannot click numerous webpages such as htttx://wtop.com, httx://wjla.com and other media websites and those sites will not let you click on anything on the webpage. And then you get the entire page becomes a link to an rdsrv.com which when clicked, complains about flash player being out of date? If you have the same problem, please read more about this post.

rdsrv.com takes over webpages


rdsrv.com will try to alter system configurations, DNS settings, registry settings, web browser settings and others to manipulate PC to the fullest and instantiate automatically whenever PC starts. It can be attached with all brands of internet browsers such as Internet Explorer, Google Chrome, and Mozilla Firefox, Yahoo, Bing.

How to Remove Trojan.Swifi – Detailed Removal of vip_117[1].swf (Trojan.Swifi)

Trojan.Swifi detected on your computer?


Trojan.Swifi is a threat that is detected by some famous antivirus programs and you know that it contains the file vip_117[1].swf (Trojan.Swifi) on C:\users\knemlick\appdata\local\microsoft\windows\inetcache\low\ie\6za21epy\ subdirectory. Trojan.Swifi has found to attack many OS like Windows XP, Vista, Seven, 8. It is one of the malignant Trojan horse viruses that can cause lots of pop-up advertisement windows uninterruptedly shown on the computer screen and CPU usage can reach to 99% with few programs running backstage. This Trojan also carries out intrusive activities on the infected computer surreptitious. This pest injects its codes into system file folder and legit programs. It also takes control over the machine right after the machine boots up with manipulation of registry files and start-up items.

Removal of http://www.hotchatdate.com/chat-us/ac/cb30602-chat-s07c.php? Pop-ups – How to Remove hotchatdate.com Pop-ups


Information about hotchatdate.com


Hotchatdate.com looks like a very legitimate website that many users may think it is a useful search for users. But this program might be used by some hackers to do something unwanted activities on the installed computers. It can attack browsers including Internet Explorer, Mozilla Firefox and Google Chrome, Yahoo, Bing and others. And then changes the DNS, homepage, search engine settings, so the default homepages, search engine to hotchatdate.com.

11/30/2014

Win32:Mobogenie-O[Adw] Completely Removal - Workable Steps to Remove Win32:Mobogenie-O[Adw]


How Win32:Mobogenie-O[Adw] Get Inside Your PC?


Win32:Mobogenie-O[Adw] can simply infiltrate into your computer without your permission and knowledge and successfully damages your all system applications. If it gets way to sneak into your machine by different ways like as:

1. When you download spam email attachments and read junk email messages.
2. When you are browse some adult or malicious domains.
3. When you click on sponsored links or ads and redirect to dubious sites.
4. Playing online games or watching movies online.
5. Peer-to-peer file sharing.