11/11/2013

How to get rid of Oxi.compdist.net pop up virus, Oxi.compdist.net popups removal tips


Your browser keeps open a page from http://oxi.compdist.net/sd/cpops-1.2.0.html?u=http%3A%2F%2Foxi.compdist.net%2Fsd%2Fapps%2Ffusionx%2F0.0.4.html%3Faff%3D1060-2030&p=TubeSing? No matter how you try to stop this pop-up from Oxi.compdist.net, it can come back again? Scan with antivirus programs but cannot find anything about Oxi.compdist.net pop ups? Please read this post, and if you have no idea to stop this popup, please contact Tee Support PC experts online 24/7 here.


Multitude pop-ups and fake alerts from Oxi.compdist.net keep popping up on your screen constantly


Oxi.compdist.net popup is a kind of malware that is connected with a type of adware and hijacker browser. It is very obvious infection for computer users that it starts to show a lot of pop-ups on the screen. Each time you open your browsers, you can get popups from Oxi.compdist.net which can disturb your work on computer. These pop-ups keep appearing on all kinds of browsers such as Internet Explorer, Mozilla Firefox or Google Chrome. If you are browsing the webpage, you can be easy to see the shown popups.

11/09/2013

How to get rid of Tube Dimmer malware, guide to uninstall Tube Dimmer


A program called Tube Dimmer installs on your computer without your notification? Tube Dimmer is compatible with your Firefox automatically? You have removed it but it keeps coming back? Your antivirus application fails to pick up this infection? You feel really upset and want to totally get rid of Tube Dimmer? Please click here to download Powerful Scanner SpyHunter to scan your computer, your problem will be fixed effectively. 

The  Image of Tube Dimmer malware


Tube Dimmer Malware Makes you Anger?


The Profile of Tube Dimmer

Name of the threat: Tube Dimmer

Threat type: malware

Affected OS: Win32 (Windows XP, Vista, Seven, 8)


Tube Dimmer is an aggressive application that can bypass the detection of antivirus program. Once installed, this program can be attached itself as an extension or plug-in to all kinds of internet browsers like Internet Explorer, Google Chrome and Mozilla Firefox. It claims to allow computer users to turn off the lights while watching videos on favorite websites such as YouTube, Facebook, and Twitter. But it in fact Tube Dimmer  is a kind of malware that can cause more problems on the installed computers.

How do I Stop Optimize-app.com Pop-ups, How do I Get rid of Optimize-app.com Redirect Virus


Suddenly, the browsers start to open Optimize-app.com without your permission? Various pop-ups from Optimize-app.com show on webpage? Each time you hit a link or open a site, you get a page to http://Optimize-app.com automatically? Have no way to remove this redirect virus? Please read more here.

The Scene of Optimize-app.com Redirect Virus


Optimize-app.com is a classified as a kind of malware that has connects with browser hijacker and adware. As long as this program comes into the target computer, it can be lurking on the system, and then adjust the infected system in the backstage. At the first of all, as a hijacker, it can change the settings of existed internet browsers. It can attack all kinds of browsers such as Internet Explorer, Mozilla Firefox, Google Chrome, Bing, Yahoo and Opera, Safari(especailly). It causes many redirections to http://Optimize-app.com or other unwanted websites. If you type any sites on the address bar, you are redirected to its own site. In such case, you cannot get any wanted search results.

11/07/2013

How do I stop uPlayer popup virus, how to block uPlayer popup ads


Do know why I keep getting popup ads from uPlayer? Want to block these uPlayer popups? Have tried many ways to stop them, but none of them has the effectiveness? Please read more here.

Be Plugged by uPlayer popup virus seriously, want to mop up?


uPlayer popup virus is also known as uPlayer Media player popup virus, uplayer media player-setup.exe virus or “You need to update your version of media player” virus. It is a very aggressive program that is a part of adware. As long as this virus comes out, it will attack all kinds of internet browsers such as Google Chrome, and Internet Explorer, Mozilla Firefox, Yahoo, Bing or Safari. And all versions of operating system can be affected including Windows2000, XP, 2007, 2008, or Mac.

Basically, once uPlayer popup virus or uplayer media player-setup.exe gets inside the target computer, it has the capability to modify the settings of the using internet browsers. In such case, victims can gain a bunch of unwanted popups that remind them to update Media player. But it is a fake message that made by some cyber criminals who want to attract users to click these popups. Most of omputer users think that popup window text as a legitimate one and click the window which redirects them to several malware sites contain more ads or links. By using this mean, the cyber criminals can gain money from it. So uPlayer popup is performed as advertisement platform which has authorized dangerous tasks along with spreading unwanted adverts.  Since users always are redirected to some malicious sites which may promote by hackers who will steal all your confidential data like account number, user name, credit card number and other private data and them use it onto the commercial purpose.

Normally, uPlayer popup can reach the target computers without permission from computer users. If users open spam email attachments, visit malicious and porn websites, download programs without paying fee, click malware popup links and ads, use infected storage devices, this virus can appear on the system. In addition, uPlayer popup can spread itself through Trojan or other malware, and it also takes advantage of loophole in the computer and the vulnerability of internet security and firewall of Windows.

The dangerous features of uPlayer popup virus


1, it is very nasty and foxy adware.
2, the settings of installed internet browsers like homepage, search engine, DNS are modified.
3, it causes redirects to its site or other sites automatically.
4, it can affect all version of Windows based operating system and all kinds of internet browsers.
5, it creates new files and registry which make your system run in a strange state.
6, a bunch of popup ads or links show on the webpage while you are surfing. 
7, this program tracks the user online and offline activities and then send them to hackers who will use it to commercial purpose.

How to get rid of uPlayer popup virus


Optional guide 1: Remove  uPlayer popup manually


1. Remove it from your computer control panel.
Windows 8
Move mouse cursor to the bottom right corner of the screen. Click Settings on Charms bar and go to Control Panel. Select Uninstall a program and remove related programs.

Windows XP
Go to Start, navigate to Settings and click on Control Panel, navigate to Add or Remove Programs, choose Programs and Features, find parking.ps related programs, and hit Remove.


Windows 7/Vista
Go to Start, navigate to Control Panel, select Uninstall a program/Programs and Features, find this program and related programs, and click on Uninstall.

2. Open Task Manager and close all running processes related with uplayer media player-setup.exe:

3. Reset your browser’s settings (take Google as an example) 

a. Click on the icon ‘Customize and control Google Chrome’, select ‘Options’.
b. Choose ‘Basic’ Options and change Google Chrome homepage to google.com or any other browser and then click the ‘Manage search engines…’ button.
c. Choose ‘Google’ and make it your default search engine.

4. Delete all registry values and infected files:
C:\Program Files\Remote Mouse\server\server.exe
C:\Windows\system32\t uPlayer.exe
C:\Windows\system32\ uPlayer.exe
C:\Windows\system32\rundll32.exe
HKCU\Software\Microsoft\Windows\CurrentVersion\InternetSettings\WarnOnHTTPSToHTTPRedirect 0\ uPlayer\
HKCU\Software\Microsoft\Windows\CurrentVersion\Settings\UID [rnd]\ uPlayer\


Optional guide 2: Remove  uPlayer popup from browser with SpyHunter


1) Click the icon to download SpyHunter


http://www.pcresolvers.com/spyhunter.php

2) Double-click on the icon the SpyHunter to open it.


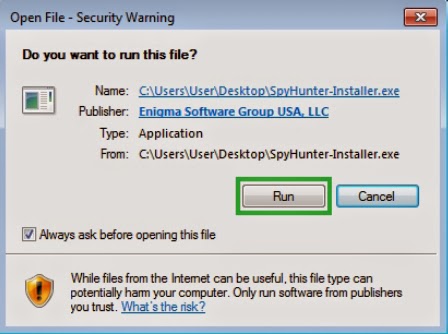
(If Windows prompts you as to whether or not you wish to run SpyHunter, please allow it to run.)
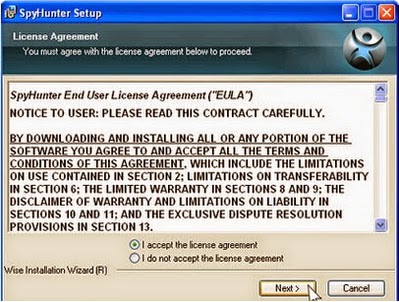
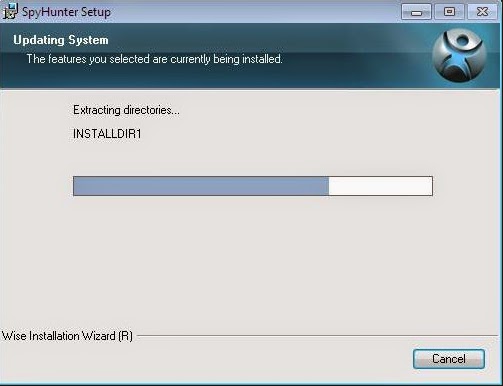
3) Click Next and complete the installation


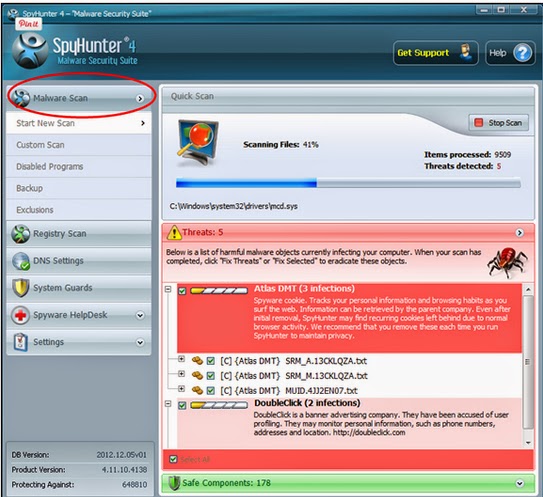
4) SpyHunter will begin to automatically scan your computer.


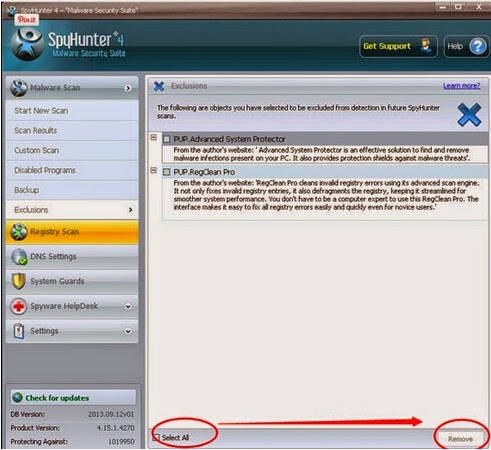
5) Click Remove button to clear up all infections.


Please keep in mind that: uPlayer popup virus is a foxy and stubborn adware which is used an adverts platform by cyber criminals. It can show up a lot of annoying popups or fake message to ask you to update your Media player. Please don’t trust any of them, and try to get rid of this adware as soon as you can. If you want to remove uPlayer popup virus completely from your attacked computer, you should find out all related files and register referred to this virus, any mistake will cause your system files missing and clash your computer down. So please click here install SpyHunter for help to stop uplayer media player-setup.exe virus.

How to remove ividi search engine completely, how to get rid of Search.ividi.org browser hijacker


Here a victim of ividi search engine;


“I tried to download something off of torrent and now the search engine "ividi" is raping my computer's browser. I've already uninstalled EVERYTHING that I could find from the control panel on my computer, and there's no extension/ add-on that I could find on the browser settings. I have internet security, scanned everything, restarted my computer... and it's still there!!”

Have tried to search everything about ividi, but cannot find anything on the control panel, and no extension or add-o? please read more this post.

The Images of  search.ividi.org


ividi search engine is raping your computer's browser?


Your original browsers search engine is replaced with ividi search engine automatically? Your default homepage is hijacked by Search.ividi.org? If you have encountered these two things on your computer, you can be sure that your browser is infected with a hijacker browser virus.

Yes, ividi search engine is a form of hijacker that looks like a legal search which contains the similar features with common search engine. But it can act a lot of undesirable activities on the installed computer. At the first sight, you can see your homepage change into http:// www.Search.ividi.org/ without your requirement at all. And your search alters into ividi search. Another obvious thing is that, various add-ons such as browser extension, toolbar, plug-in come up with ividi application. In addition, numerous shortcuts, icons and new files will be created. Otherwise, you may experience browser freeze and crash randomly, and you need to take longer time to load webpage. Moreover, a ton of popup ads or links from Search.ividi.org jump on the web page when you are surfing online.  

11/05/2013

How do I stop redirecting to get-new-java.com Webpage Virus, how to block http://get-new-java.com/index.php?dv1=Ybrant%20Digital pop-ups


A fake java update page pops up on the screen when you open Google Chrome? An address from http://get-new-java.com/index.php?dv1=Ybrant%20Digital shows up if you type a site in search box? In thepopup window, you are asked to upgrade java? You don’t know if the message is a reliable one or not, and close it. In a few minutes, more and more popups display continually. You feel unhappy and try many means to get rid of get-new-java.com redirect from your computer? Please take it easy and see more details from this post. 


The screenshot of  get-new-java.com 


A java update page from get-new-java.com pops up, is it reliable?


The answer to the question is No, it is not a reliable page, and please don’t believe any words on the pop-up windows. It is a fake java update page which has nothing with Java update in your system.
Do you discover a truth that, whenever you tan a new search or open a site which you often do the same thing as before, a webpage with texts “” pops-up on your screen, and if you don’t click OK button, you cannot do anything on your computer, for mouse is freezing. If you skip the step of assuming, you are preventing from accessing the next steps. The best way to ignore it is to close the displaying page http://get-new-java.com/index.php?dv1=Ybrant%20Digital.

Here are several victims of get-new-java.com pops up:


“Every so often when I type in a website and press enter, instead of the website I originally typed in I get redirected to this (obviously) fake java update page but sometimes it uses another address. It basically says that my java is out of date and needs to update. The first time I saw it I thought it was just a normal popup and immediately closed it but it's been showing up more and more frequently alerting me the fact that it is a virus. I've probably had this virus for about a month now as I didn't realize it was an issue until I noticed it continually popping up. Any help on it's removal would be appreciated.”


“I visit a variety of websites and more often than not I keep encountering http://get-new-java.com/index.php?dv1=Ybrant%20Digital. This page says that an out of date plug-in has been detected and to install the latest update, but this to me is strange as usually, the browser will provide a prompt and not an actual webpage. Does anyone know anything about this?”

Have you seen the complaints from the attackers? Do you still feel confused that is it a safe thing? Please read the rest post.

Why I keep getting redirected to http://get-new-java.com/index.php?dv1=Ybrant%20Digital or other address?


As we can see that, if we try to open a website or tab a new search on the search box, a page from http://get-new-java.com/index.php?dv1=Ybrant%20Digital or another similar address page opens up automatically. It the page, we can find sayings that java is out of date and needs to updated in your computer. If we try to shut down these redirect pages, but it pops up immediately and shows up new tab frequently.

Why redirections to get-new-java.com keep happening? Based on the computer security experts, it is a malware program that is from browser hijacker and adware. So it can later the affect settings internet browser such as Internet Explorer, Google Chrome and Firefox. As the modifications of settings, victims can get a bunch of annoying redirects to http://get-new-java.com/index.php?dv1=Ybrant%20Digital or its connected sites. The main goal of making this program is to gain profits by cyber criminals who want to cheat computer users who easily believe the fake popups and to click update button of fake java. In addition, hackers can utilize of this malware program to get closed to the victims and collect their online activities and steal some significant information on the attacked system. In the future, these vicious people can use the information for commercial purpose.

11/04/2013

How to block http://dlvr.readserver.net popup, how to remove http://dlvr.readserver.net redirect virus


I don't know why I keep getting multiple pop ups from http://dlvr.readserver.net/ when I open my Mac yesterday? Whenever I tab new page or click on a text box on a webpage, http://dlvr.readserver.net/bp?section=2300&type=autopop&layer=1 pens up without my permission? I have tried many tutorials online, but no one is useful? I really want to stop these pop ups, does anyone could help me? If you are a victim of dlvr.readserver.net, please read this post.


Why multiple pop ups from http://dlvr.readserver.net/ show on your Windows/Mac?


Here a case who has attacked by dlvr.readser.net redirect virus:


"  I am trying to remove this http://dlvr.readserver.net/bp?section=2300&type=autopop&layer=1 that keeps popping up when I open safari."


Commonly, dlvr.readserver.net redirect is first found to attack the computer users who have Apple (MAC OS X), but according to the complaints from victims from all over the world, it can know that this program seems to affect not only the MAC OS X but also the Windows OS. It is a malicious program that is connected with hijacker browser and adware that start to cause various issues on the infected computers.

In the sense of hijacker browsers, dlvr.readserver.net mainly attacks the existing internet browsers like Safari (for Mac), Mozilla Firefox, Google Chrome, and Internet Explorer. This hijacker can modify your original internet browsers settings such as homepage and search engine. As soon as these changes happen, your favorite homepage is hijacked by http://dlvr.readserver.net/, so that each time you open a new site and click on a text box in any browsing web page, you are keeping redirecting to http://dlvr.readserver.net/ or http://dlvr.readserver.net/bp?section=2300&type=autopop&layer=1 or other related sites without your controlling. When you browsing a page, a new tab from dlvr.readserver.net can open up by itself.